Security is not a feature. It is the architecture.
Bernio answers the confidentiality demands of privileged work through architecture rather than contractual promises — because a promise is only worth the counterparty behind it.
Four properties, enforced in infrastructure.
- Control boundary
- Which models may see a matter is set by policy, per firm, matter and task. Where the policy permits an external call, the request is de-identified first, the routing decision is recorded, and the external share is reported against a budget you set. In your own infrastructure and on Bernio Pro, the policy can exclude external models entirely.
- Architectural isolation
- The matter boundary is applied before any retrieval or model call — in the runtime, not in application logic. Ask us to show you where.
- Evidentiary audit
- Every action is appended and signed: who ran what, on which matter, with which model version, and who approved it. Where an erasure obligation applies, the entry is cryptographically severed rather than rewritten. In your own infrastructure and on Bernio Pro the log sits on your hardware; on Bernio Cloud it exports in full at any time.
- No training on your data
- Client material does not train or fine-tune any model — ours or a provider’s. Matter environments are provisioned separately and agent memory is sealed at close. On Bernio Pro configured for isolated operation, no external model sees client material at all.
The same operating system, at three levels of control over your data.
The matter model, the approval gates, the signed record and the multi-model routing are the same on every tier. What changes as you go up is custody — who physically holds the data, and how far the inference can travel.
Bernio Cloud
Available nowThe full platform, hosted and run by us. Nothing to install, nothing to operate.
Custody
Data sits in the Bernio region you select, encrypted at rest, under a processing agreement.
- The same matter model, approval gates and signed record as every other tier
- Multi-model routing under a policy you set per firm, matter and task
- Your log is exportable in full at any time
Your infrastructure
Available nowThe same platform, deployed into your data centre or your private cloud.
Custody
Your storage, your keys. External model calls can be disabled entirely by policy.
- No new data processor for your security team to vet
- The audit log is written and held inside your environment
- Retention and erasure are yours to set
Bernio Pro
In engineering — not yet availableThe platform on a dedicated appliance, with models running on the device itself.
Custody
The data and the inference stay in your physical custody. Configured for isolated operation, the network path is removed.
- Matter work continues without connectivity
- Modules that depend on outside sources pause and resume when you reconnect
- The strongest form of the confidentiality argument — and the reason it is worth waiting for
Row by row
Say which tier you are buying.
Most of what a security review asks about depends on where Bernio runs. Rather than make one claim and qualify it later, here is what each deployment actually does — including where it does less.
Bernio Cloud
Available
Your infrastructure
Available
Bernio Pro
Engineering prototype
Where inference runs
Bernio-operated environment, region of your choice
Your data centre or private cloud
On the appliance, inside your perimeter
External model calls
Policy-controlled per firm, matter and task
Policy-controlled; can be disabled entirely
None, when configured for isolated operation
Matter data at rest
Encrypted in the Bernio region you select
Your storage, your keys
On the appliance, in your physical custody
Offline operation
No
No
Yes — matter work continues without connectivity
Monitoring module
Full
Full
Requires connectivity; pauses and resumes offline
Bernio administrative access
Yes, scoped and logged
Optional, scoped, logged and revocable
Optional, revocable; none in isolated operation
Update path
Continuous
Scheduled with your change process
Signed media, customer-initiated
Bernio Pro is an engineering prototype: the appliance runs, and it is not yet available for customer deployment. Where this site makes a claim that holds only on the appliance, it says so beside the claim. Cloud and private deployments are in production today.
Development status
Bernio is in active development with design partners — firms running real matters through the platform and shaping what is built next — and the first commercial contracts are being signed on founding terms. The capabilities described on this page are built and can be demonstrated on a matter type your team handles. Bernio Pro — the on-premise appliance — is an engineering prototype and is not yet commercially available, so any capability on this site that depends on it is marked as such. Descriptions of the product are not warranties; the binding terms for any deployment are those set out in the applicable written agreement.
The controls, and the tier each one holds on.
Bernio is architected for the obligations legal teams carry — to clients, to regulators, and to the profession itself.
Isolated data environments
Per client and matter, applied in the runtime before any retrieval or model call rather than in application logic. Matter environments are provisioned separately and agent memory is sealed at close — on every tier. Where the environment itself must be yours, that is the on-premise tiers.
Full audit logging
Who ran what, when, on which matter, with which model version. Append-only and signed; where an erasure obligation applies, the entry is cryptographically severed rather than rewritten. In your own infrastructure and on Bernio Pro the log is held on your hardware; on Bernio Cloud it is exportable in full at any time.
De-identified before it leaves
Party names, client identifiers and firm identity are removed from any request routed to an external model, and what was sent is recorded. This is pseudonymisation, not anonymisation — which is why the default is to keep the work on the models Bernio operates, and why in your own infrastructure and on Bernio Pro external calls can be switched off entirely.
No training on your data
Client data does not train or fine-tune a model — ours or a provider’s. Matter environments are provisioned separately and agent memory is sealed when a matter closes. On Bernio Pro configured for isolated operation, no external model sees client material at all.
Built for the obligations you carry
Rule 1.6 and Opinion 512 bind you, not your software. Bernio is architected so the reasonable-efforts showing is something you can evidence — where inference ran, who approved what, on which version.
You keep the record
Your audit log exports in full at any time, on every tier. In your own infrastructure and on Bernio Pro you hold the storage and the keys outright, so audit, administration and model availability do not depend on our continued cooperation.
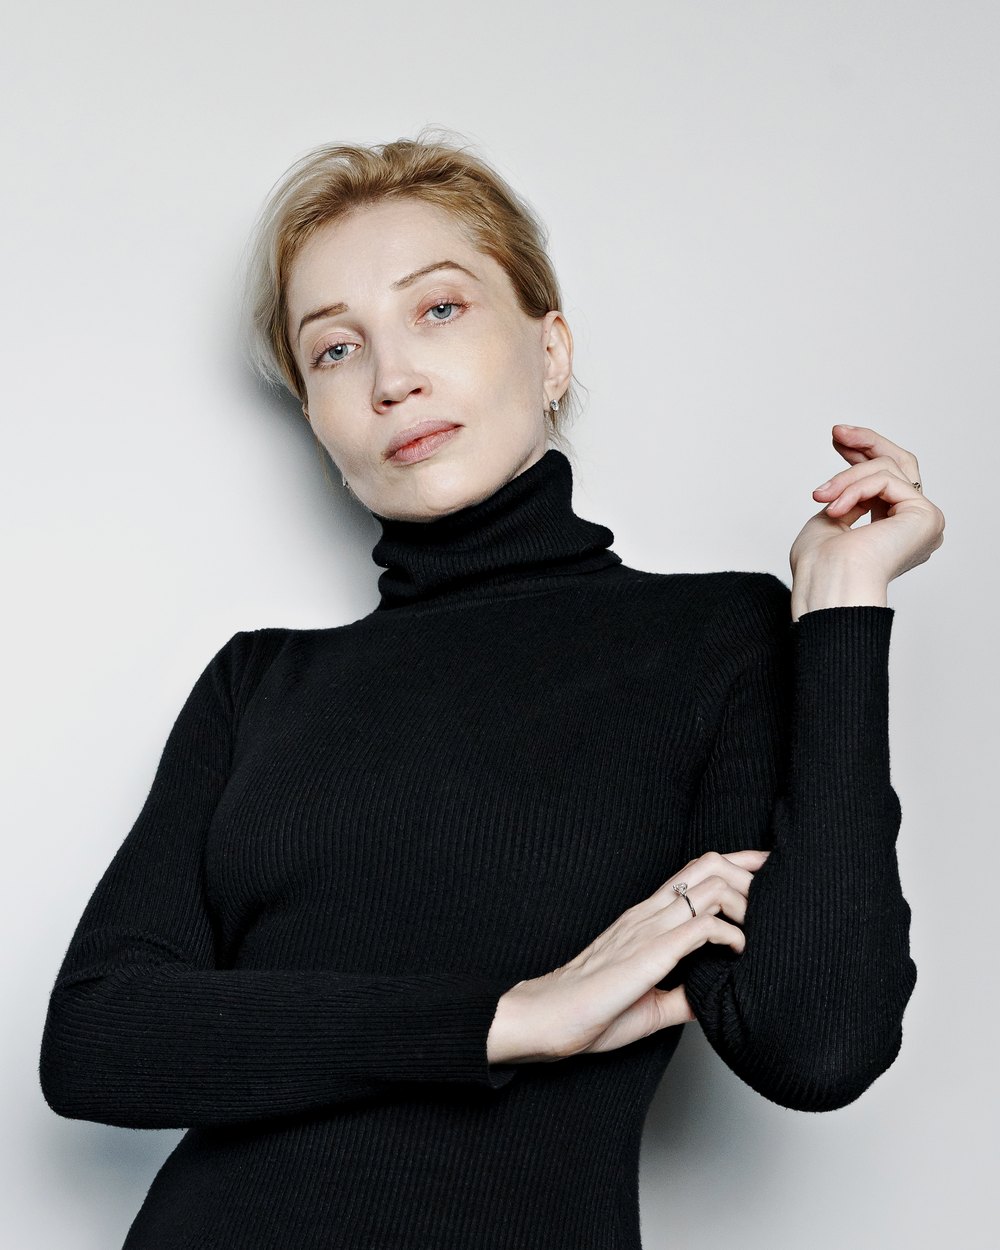
Dr. Alexandra Carl Bernadotte
Co-Founder & Chief Technology Officer
AI · Cryptography · Systems engineering
Security is an engineering property, not a policy document.
"A confidentiality guarantee that depends on a vendor behaving well is not a guarantee — it is a hope with a contract attached. We build the ones that hold whether or not anyone is watching."
Most legal AI is an application sitting on somebody else’s inference. That is a reasonable way to build software and a poor way to handle privileged material, because every meaningful control ends up living in a contract rather than in the system. Bernio is built the other way round: the matter boundary is enforced in the runtime before any retrieval or model call, the audit trail is signed on hardware the firm controls, and the routing decision for every inference is recorded whether it stayed local or not.
That design comes from a research background where the constraint was never optional. Our team’s work spans machine learning under hardware constraints, applied cryptography, and secure systems engineering, including years of shipping models into environments where a wrong answer is a critical event rather than a bad draft. Building for a regulated profession is a familiar problem to us, not a new one.
A small model built for legal structure, not for conversation.
Frontier models are extraordinary generalists. They are also large, metered, and hosted by someone else — which makes the three things a firm actually needs expensive: running inference inside your perimeter, isolating memory per matter, and reproducing an output six months later. We train our own small language models for the legal tasks that make up most of the work.
It runs where the file already is
Small enough to serve from hardware a firm can own, so the default path involves no egress at all — and the confidentiality argument stops depending on a processing agreement.
Isolation becomes affordable
Per-matter memory isolation is trivial to promise and expensive to deliver on a hosted frontier model. On models we run ourselves, an isolated instance per matter is an ordinary deployment decision.
Tuned to legal structure
Clause boundaries, citation form, date precision, custodian and privilege state — the units legal work is actually made of. A general assistant treats a chronology as prose; ours treats it as a typed record with sources attached.
Reproducible, and therefore auditable
Version-pinned and retained, so the model that produced an output is still available to explain it — held in your environment on the on-premise tiers. A hosted model that has since been retired cannot be re-run against the record it created.
Cost that does not move
Compute you own rather than tokens you meter. Volume becomes a capacity question rather than a vendor-controlled line item.
Frontier models still do the heavy reasoning where a firm’s policy permits it — routing is per task, not per ideology. We are preparing our evaluation methodology and results for publication in Research, and we will show a firm the same numbers computed on its own matters during evaluation.
The state of the controls, reported by the platform itself.
A security questionnaire is answered from a screen, not from a slide. The firm view shows the audit trail sealed, conflicts and AML clear, and where inference actually ran.
- Audit trail state reported continuously, not assembled for a review
- Conflicts and AML clearance visible at the firm level
- Local-first routing, with the external share measured against budget

Everything on this page, in a form your security team can file.
The architecture argument is above. The Trust Center is the evidence behind it — written for a reviewer filling in a questionnaire rather than for a reader being persuaded. It publishes shortly; until it does, we send the same material directly, within one business day.
Model providers
Every external model that can be called, what it is used for, where it processes, and how to switch it off.
Subprocessors
Who else touches anything, for what, and in which region — with advance notice of changes written into the DPA.
Certification status
Where SOC 2, ISO 27001 and penetration testing actually stand today. Including the ones we have not started.
Documents
DPA, standard contractual clauses, technical and organisational measures, and our answers to the CAIQ.
The infrastructure your practice deserves.
We are taking on design partners: firms that run real matters through Bernio, shape what gets built next, and come in on founding terms. We run the demo on a matter type your team handles.